I've sat in the
hot seat.
Now I help you
stay out of it.
Leading security programs since 2006 taught me what the textbooks do not cover. What it feels like when the board is waiting, the auditors are circling, and your program isn't ready. Corvus exists because organizations deserve better than checkbox consulting.
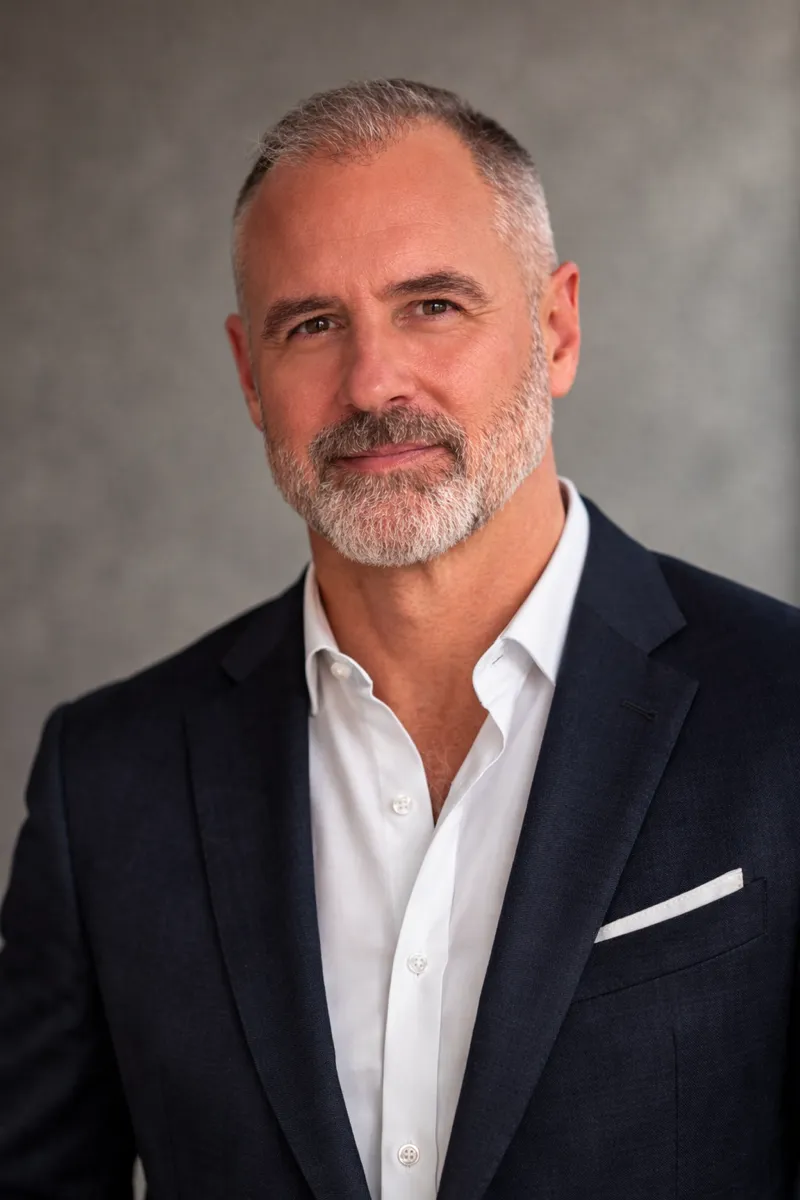
Built from inside the role.
I started my career in security long before “CISO” was a common title — back when you were the person who said “we shouldn’t do that” in a room full of people who didn’t want to hear it. Since then I have held the seat in state government, higher education, tribal government and gaming, and B2B SaaS. I built programs from scratch, rebuilt programs that were quietly failing, and stood in front of boards to explain incidents I didn’t cause but was responsible for fixing.
“I’ve seen what happens when a security program is built by someone who’s never had to defend it at 2 AM.”
That experience taught me something the consulting industry consistently gets wrong: security advice without operational accountability is just theory. Firms that have never run a program, never managed a breach response, never faced a QSA on the other side of the table — they give you frameworks. They give you deliverables. They give you a report and a handshake.
I founded Corvus to do something different. Every engagement I take on, I’m the practitioner in the room — not a junior analyst following a checklist. When I recommend a control, I have owned the program it sits in. When I prepare you for an audit, I have been through those audits as the person responsible for the result. When I tell you what the board needs to hear, I have delivered that briefing to boards, audit committees and tribal leadership.
The decision to build Corvus full-time wasn’t a sudden one. My view is that mid-market companies, production studios and PE-backed firms struggle to get meaningful security leadership without the overhead of a full-time executive hire. The vCISO model existed, but too often it meant a part-time consultant showing up once a quarter with a slide deck.
That’s not what organizations actually need. They need someone who answers the phone when the auditor calls unexpectedly. Someone who knows their business risks, not just their security controls. Someone who can translate a threat briefing into a budget conversation without losing either audience.
“Your security program should make your business stronger — not just make auditors comfortable.”
Corvus is the practice I wished existed when I was on the other side of the table, trying to find a partner I could actually trust. We work with a focused set of clients, go deep on each engagement, and measure our success by one thing: whether your organization is genuinely more secure and more resilient than when we started.
If that’s what you’re looking for — not a vendor, not a checkbox, but a practitioner who’s been exactly where you are — I’d like to talk.
Why Corvus.
Our name comes from Corvus, the genus of ravens and crows, birds known across cultures for their intelligence, vigilance, and adaptability. Ravens are problem solvers. They recognize patterns, anticipate threats, and adapt in ways that consistently outpace their environment. That is the standard we hold ourselves to on every engagement.
A raven doesn't react to danger. It sees it coming.
The path that built the practice.
Held security leadership roles across state government, higher education, tribal government and gaming, and B2B SaaS. Board-level reporting, program ownership, and incident command.
Led audit programs across SOC 2, PCI DSS, SOX ITGC, GovRAMP, TX-RAMP and GLBA, including the first SOC 2 Type II attestation for a newly acquired business unit.
Led cyber diligence and integration security across the deal lifecycle: sell-side, buy-side and post-merger integration.
Built the vendor risk program for a higher-education SaaS company, covering about 300 vendors, with AuditBoard as the platform of record.
Translated technical risk into business language for C-suite, audit committees, and board directors. Developed security KPIs and risk dashboards for executive audiences.
Fractional vCISO and GRC consulting practice serving media production, financial services, healthcare, and technology clients across Southern California and beyond.
The principles behind every engagement.
Practitioners, Not Consultants
I have owned the programs I advise on. When I recommend a control framework, a vendor, or a remediation path, it is because I have run it and defended it in a real audit. No textbook theory, no generic best practices. Lived experience only.
No Upsell Culture
Corvus doesn’t have a products division to cross-sell or a staffing bench to fill. My only incentive is your outcome. If you need a $5,000 gap assessment and not a $50,000 retainer, I’ll tell you that. Your trust is worth more than a larger invoice.
Audit-Tested Methods
The programs I have built have been through real audits. I know what QSAs look for. I know where Type II assessors push back. I build programs to survive scrutiny, not just to satisfy checkboxes.
Fixed-Scope Engagements
Every engagement has clear deliverables, a defined timeline, and transparent pricing before work begins. You will never receive a surprise invoice from Corvus. Ambiguity in scope is my problem to solve before we start, not yours to absorb at the end.
Every engagement starts with a no-cost discovery call.
Tell me what you’re facing — an upcoming audit, a board presentation, a program that needs rebuilding, a deal that needs a security lens. I’ll tell you honestly whether Corvus is the right fit, and what a first step looks like.
No sales pressure. No obligation. Just a straight conversation with a practitioner who’s been there. Grab a time directly below — no back-and-forth required.
🔒 NDA available upon request · Responses within one business day
Prefer email?
We respond within one business day · No spam · No obligation